Data Compliance
From the book I Am Datapedia!, published here free by the author.
Data Compliance is mostly confused with Data Quality and Data Integrity, which is somehow true, as all these terms do share some common features for ONE GOAL i.e., Data Protection.
Data Compliance is to follow certain regulations and standards of Data Security, Data Privacy and Data Integrity, set by different Regulatory Bodies around the World to protect sensitive data and to make data available in certain ways.
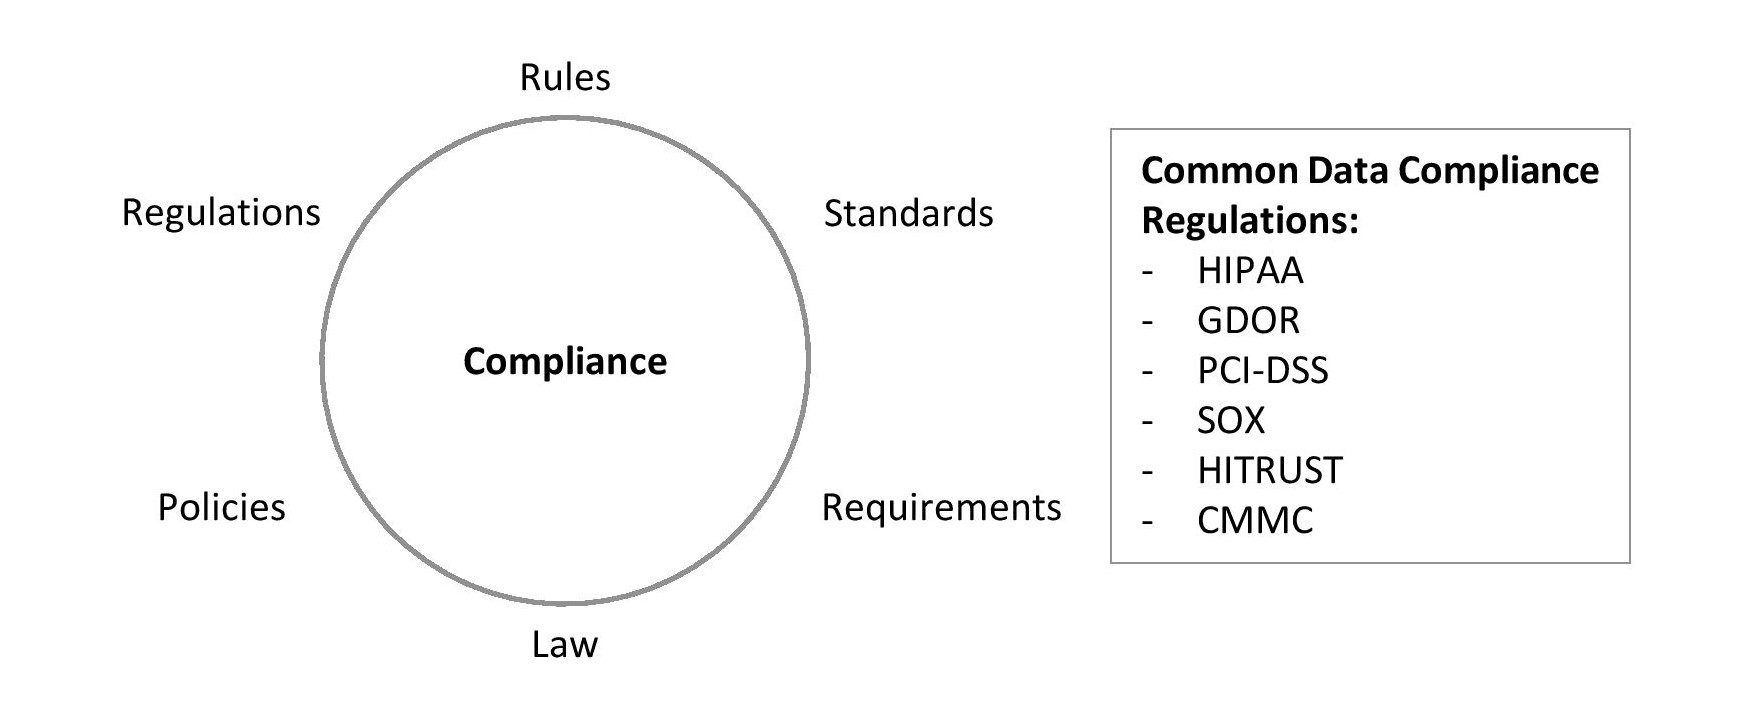
Common Regulatory Bodies Frameworks
We won’t be going into details of regulatory bodies like what is required by each but for the audience, let me mention the most famous ones here.
- GDPR
- HIPAA
- PCI DSS
- SOX
- CCPA
- CMMC
How Do You Ensure Data Compliance?
- Conduct regular periodic revisions to set latest measure for data protection.
- Maintain all the data protection measures and all the audit procedures.
- Assign a SPOC (single point of contact) or a department to host and maintain data security and compliance standards.
- Always used commonly used Frameworks
Please note, regulatory policies, procedures, workflows, and operational requirements differ in different countries. It is very important to understand that one needs to follow the law of the country where the data is generated. Accessing data cross border raises Data Sovereignty concerns.
Express your reaction
Your Take on This Insight?
Share how this content resonates with you.
0 reactionsSign in to react or comment
Comments (0)
No comments yet.
Free account
You can read every topic without one. A free account lets you react to this topic, comment under it and search the Knowledge Hub. Reacting and commenting need a confirmed e-mail address.